Short answer: for a startup that needs SOC 2 or ISO 27001 without a compliance person on staff, the best Vanta alternative is Probo: an open-source platform plus a dedicated compliance officer for $10,000 for the year, built for AI agents with GraphQL, MCP and a CLI. If you already have a security team and want a self-serve tool, Drata and Secureframe are the closest alternatives.
You just got the email from your biggest prospect's security team. "Please complete the attached vendor security questionnaire and provide your SOC 2 report."
You don't have a SOC 2 report.
So you start researching compliance platforms. Vanta is everywhere. Every Y Combinator batch mentions it. Every "how we got SOC 2" blog post features it. You sign up for a demo, get quoted $15,000+/year, and realize: you still have to do all the work yourself.
That's the part nobody tells you upfront.
Vanta is a dashboard. It plugs into hundreds of integrations that pull far more evidence than an auditor needs, and hands you template policies and the same control set it gives every customer. At the end of the day, you're the one adapting those templates, mapping controls, chasing your team for access reviews, and figuring out what the auditor actually wants.
For a 200-person company with a dedicated security team, that's fine. For a 15-person startup trying to close its first enterprise deal, that's a full-time job nobody budgeted for.
This article compares 7 Vanta alternatives honestly. No affiliate rankings. No "they're all great!" hedging. We'll tell you who each platform is actually built for, what it costs, and where it falls short.
Disclosure: Probo publishes this page and sells one of the options below. Probo comes first because it is the only option that combines an open-source platform, a dedicated compliance officer and native access for AI agents. For every other platform, we say who it fits better than Probo.
The real question: tool vs. service
Before we compare platforms, let's reframe the decision most founders get wrong.
The question isn't "which compliance automation tool should I buy?"
The question is: "Do I need a tool, or do I need someone to do the work?"
Most compliance platforms sell you software and assume you have someone internally who knows what to do with it. That's a massive assumption. If you don't have a compliance person on staff, buying a compliance tool is like buying a professional camera and expecting it to make you a photographer.
Some of the platforms below give you the camera. One of them sends you the photographer.
Keep that distinction in mind as you read.
The comparison table
Here's the honest side-by-side. We scored each platform on five criteria that actually matter when you're evaluating alternatives to Vanta.
| Platform | Starting Price | Open Source | Human Expert Included | You Do the Work | Best For |
|---|---|---|---|---|---|
| Probo | Free (self-hosted) / $10K/yr (platform + service) | ✅ Yes | ✅ Dedicated compliance officer | No — they do it | Startups that want compliance done, not managed |
| Vanta | ~$15K–$25K/yr | ❌ | ❌ (partner network) | Yes | Mid-market teams with in-house security |
| Drata | ~$15K–$22K/yr | ❌ | ❌ (partner network) | Yes | Companies wanting strong automation + GRC |
| Secureframe | Custom (quote-based) | ❌ | ❌ | Yes | Teams needing federal/DoD compliance (CMMC) |
| Scytale | Custom (quote-based) | ❌ | ✅ Optional consulting bundles | Partially | Startups wanting a bundle (platform + pen test + consulting) |
| Sprinto | Custom (quote-based) | ❌ | ❌ | Yes | Budget-conscious teams outside the US |
| Thoropass | Custom (quote-based) | ❌ | ✅ In-house auditors | Partially | Companies wanting audit + platform in one vendor |
1. Probo: compliance done for you, built for AI agents
What it is: An open-source compliance platform backed by Y Combinator, with an optional full-service tier where a dedicated compliance officer runs your entire program.
Why it's first on this list: Probo is the only platform here that you can deploy for free today and self-host. It's also the only one where, if you choose the managed plan, a real compliance officer writes your policies, talks to your auditor, and handles evidence collection for you.
That's not a chatbot. That's not a "partner network" you get referred to. That's a person assigned to your company who manages the entire lifecycle.
Built for AI agents: Probo is designed so AI agents can work on your compliance program together with your team and your compliance officer. Everything is available through a full GraphQL API, an MCP server with 400+ tools (Claude, ChatGPT, Cursor, VS Code and more) and the prb CLI. An agent can review risks and controls, draft policies, answer security questionnaires or update vendor reviews, always within the permissions of the person who connected it.

What you actually get:
- • Open-source self-hosted tier: Framework tracking (SOC 2, ISO 27001, GDPR, HIPAA, and more), automated evidence collection, community support. Free. Forever. No vendor lock-in.
- • Platform + service ($10,000/year): The Probo platform plus a dedicated compliance officer for the year: gap assessment, risk analysis, vendor reviews, custom policies, audit prep and representation.
- • Enterprise (custom): Bring your own cloud, forward-deployed compliance engineer, custom frameworks, physical presence during audits.
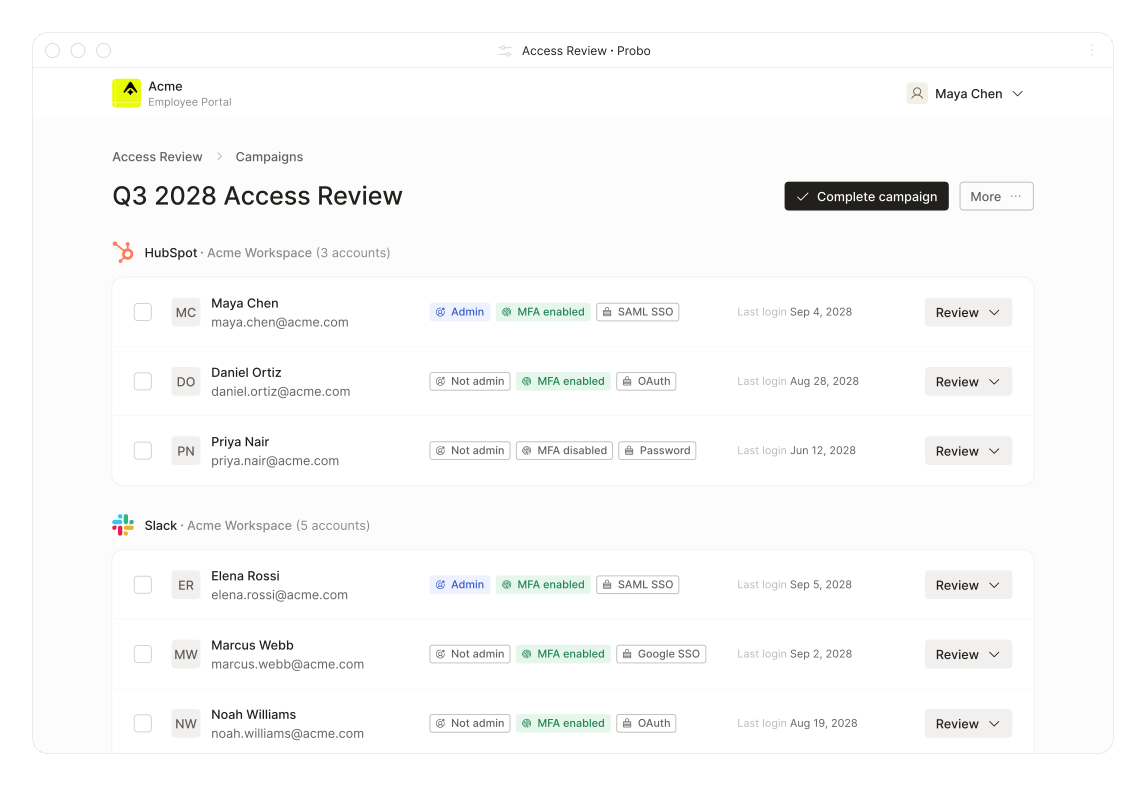
Time to audit-ready: It depends on your setup. A small team with a standard stack can be ready in 2 to 4 weeks, because experts do the work and follow up with you, instead of you learning a new tool and guessing whether you're ready to book the audit.
The honest downside: Probo is built for startups and SMBs. If you're a 2,000-person enterprise running 15 frameworks across global subsidiaries, you'll outgrow the current offering. They're scaling fast, but the sweet spot today is teams under 500 people.
Frameworks: SOC 2 (Type 1 & 2), SOC 3, ISO 27001, ISO 27701, ISO 42001, GDPR, HIPAA, CCPA, FERPA, CASA.
"We worked with Vanta in the past and didn't like the experience, but switching to Probo was night and day." — Pierre de Poulpiquet, Co-founder & CTO at Whaly
For a detailed head-to-head, read our full Probo vs Vanta comparison.
2. Vanta: the market leader you're probably comparing against
What it is: The largest compliance automation platform, now positioning itself as an "agentic trust platform" with AI features across policy generation, evidence checks, and questionnaire automation.
Who it's actually for: Mid-market and enterprise companies (100–5,000 employees) that already have someone internally who understands compliance and needs a tool to manage it at scale.
What you get:
- • Essentials: One compliance framework, AI agent for policy generation, automated evidence collection, trust center, auditor API.
- • Plus: Everything above plus AI-powered questionnaire automation (25/year), access management, expanded AI features.
- • Professional: Questionnaire automation (144/year), risk management, advanced trust center, custom monitoring tests, advanced reporting.
- • Enterprise: Fully customizable.
Pricing: Not listed publicly. Expect $15,000–$25,000/year for a startup-sized deployment, scaling higher with headcount and frameworks. Multi-year contracts are common. Vanta doesn't publish prices — you have to sit through a demo to get a quote.
The honest downside: Vanta gives you the cockpit. You still need to fly the plane. Policy writing, control mapping, auditor communication, evidence gap remediation — all on you. If you're a first-time founder who doesn't know the difference between SOC 2 Type 1 and Type 2, Vanta won't teach you. It'll show you a dashboard full of red indicators and wish you luck.
The "partner network" for additional compliance services means Vanta refers you to external consultants for the actual work. Those consultants cost extra — often $10,000–$50,000 on top of your Vanta subscription.
Frameworks: 30+ including SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CMMC, and more.
3. Drata: strong automation, enterprise ambitions
What it is: A compliance automation platform that's been pushing hard into enterprise GRC territory. Now brands itself as "The Agentic Trust Management Platform." Trusted by 8,000+ customers.
Who it's actually for: Growth-stage companies (50–1,000 employees) that want deep integrations and are building out a formal security program.
What you get:
- • Automated evidence collection with continuous monitoring
- • Cross-framework control mapping (map once, reuse across SOC 2, ISO 27001, etc.)
- • Trust center with AI-powered responses
- • Questionnaire automation
- • Third-party vendor risk management
- • Enterprise GRC capabilities
Pricing: Not public. Comparable to Vanta — roughly $15,000–$22,000/year for startups. Enterprise deals go significantly higher.
The Vanta vs Drata verdict: If you're comparing Vanta vs Drata head-to-head, the products are more similar than different. Both pile on integrations most startups don't need, and both start from the same templated policies and controls for every customer. Both leave you doing the work. That is the same one-size-fits-all problem we wrote about earlier. Pick based on which sales team gives you a better deal. Seriously.
The honest downside: Same core problem as Vanta. It's a powerful tool, but you need to know what you're doing. The "Agentic AI" branding is heavy on marketing, lighter on substance — most of the AI features are copilots that draft content for you to review, not autonomous agents that run your compliance program.
Frameworks: SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CCPA, and 20+ more.
For a broader landscape view, see our Top 5 GRC Tools in 2026 comparison.
4. Secureframe: the federal compliance play
What it is: A compliance platform that's carved out a niche in federal and defense compliance (CMMC, FedRAMP) alongside the standard SOC 2/ISO 27001 offerings.
Who it's actually for: Companies selling to the US federal government or defense contractors, plus standard SaaS companies that want a Vanta alternative.
What you get:
- • Fundamentals: One framework, infrastructure monitoring, evidence collection, policy management, risk management, trust center.
- • Complete: Advanced third-party risk management, advanced user access reviews, questionnaire automation, SSO/SCIM.
- • Defense: Everything above plus SPRS score tracker, System Security Plan (SSP), Plan of Action & Milestones (POA&M), managed CUI enclave, managed virtual desktops.
Pricing: Quote-based. Expect similar range to Vanta/Drata for commercial frameworks. Defense tier is premium.
The honest downside: If you don't need federal compliance, Secureframe doesn't offer much that Vanta and Drata don't. The Defense tier is genuinely differentiated and useful if you're pursuing CMMC. For standard SOC 2 or ISO 27001, it's a solid but undifferentiated option.
Frameworks: SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CMMC, FedRAMP, NIST 800-53, and more.
5. Scytale: the all-in-one bundle
What it is: A compliance platform that bundles software, consulting, and penetration testing under one roof. Based in Israel, growing fast internationally.
Who it's actually for: Startups that want to buy everything from one vendor — platform, consulting, pen testing — without stitching together three different contracts.
What you get:
- • Build Starter: Platform + 1 framework.
- • Build DFY (Done for You) : Platform + consulting (LaunchReady plan) + pen test (web app, black box). Most popular bundle.
- • Build Stronger: Platform + ongoing consulting (StayReady plan) + pen test (gray box).
- • Scale/Enterprise: For security teams wanting custom frameworks, on-prem integrations, advanced SLAs.
The honest upside: Scytale is the only platform besides Probo that offers an actual "done for you" option with consulting baked in. Their LaunchReady consulting plan assigns a dedicated consultant for up to 6 months. The StayReady plan extends to 12 months with ongoing compliance tracking.
The honest downside: "Done for you" at Scytale means a consultant guides you. At Probo, it means a compliance officer does the work. There's a meaningful difference. You'll still spend significant internal time on Scytale's DFY plan, especially during implementation. Also — no free tier, no open source.
Frameworks: SOC 2, ISO 27001, HIPAA, GDPR, SOX-ITGC (Enterprise), and more.
6. Sprinto: budget-friendly, automation-first
What it is: A compliance automation platform popular with startups in India and Southeast Asia, increasingly expanding into US/EU markets.
Who it's actually for: Budget-conscious startups that want SOC 2 or ISO 27001 quickly and don't mind a DIY approach.
What you get:
- • Automated evidence collection
- • Continuous monitoring
- • Pre-configured compliance programs
- • Built-in security training
- • Audit dashboard and readiness checks
- • AI-powered features (Sprinto AI)
Pricing: Not publicly listed (password-protected pricing page). Historically positioned below Vanta and Drata — expect $8,000–$15,000/year based on market reports.
The honest downside: Smaller auditor network. Template-driven like Vanta and Drata. Customer support quality varies based on time zones.
Frameworks: SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and others.
7. Thoropass: auditor + platform under one roof
What it is: A compliance platform that also employs in-house auditors (former Big 4 and Coalfire). They do the audit themselves instead of connecting you with a third-party firm.
Who it's actually for: Companies that want to simplify procurement by buying platform + audit from the same vendor.
What you get:
- • Compliance automation platform with 300+ integrations
- • In-house audit team (KPMG, EY, Coalfire alumni)
- • AI-powered evidence validation
- • Multi-framework support (30+ frameworks)
- • Pen testing, managed CUI enclaves (for defense)
Pricing: Not public. Premium positioning — expect Vanta-level pricing or higher since audit fees are baked in.
The honest downside: When the platform vendor and the auditor are the same company, independence becomes a question. Thoropass addresses this with separate internal teams, but some buyers (and their customers' security teams) prefer a clear separation between the tool that collects evidence and the firm that audits it. Also — no free tier, no open source.
Frameworks: SOC 2, ISO 27001, HIPAA, PCI DSS, HITRUST, GDPR, CMMC, FedRAMP, and 30+ more.
Not sure which compliance framework you need?
Take the free compliance framework recommender — answer a few questions about your business, and get a personalized report telling you exactly which certifications to pursue first.
So which Vanta alternative should you pick?
"I have a security team and just need a better tool."
→ Drata or Secureframe. Both are mature, well-integrated, and functionally similar to Vanta. Negotiate hard on price.
"I need federal/defense compliance (CMMC, FedRAMP)."
→ Secureframe's Defense tier is purpose-built for this.
"I want to bundle platform + consulting + pen test."
→ Scytale's DFY packages simplify procurement.
"I want the auditor and platform from one vendor."
→ Thoropass. Just think through the independence question.
"I'm a startup, I don't have a compliance person, and I need to get SOC 2 or ISO 27001 done without it consuming my engineering team."
→ Probo. Deploy the free open-source version to explore, or take the platform + service plan ($10,000/year) and let a compliance officer handle everything. Audit-ready in as little as 2 to 4 weeks, depending on your setup.
"I want AI agents to work on our compliance alongside the team."
→ Probo. Every record is available through GraphQL, MCP and the prb CLI, so Claude, ChatGPT or Cursor can work on risks, controls, policies and questionnaires with your team and your compliance officer.
"I just want to see what compliance looks like before spending money."
→ Deploy Probo for free. It's open source. No credit card, no sales call, no trial expiration.
Frequently asked questions
What is the best Vanta alternative for a startup?
Probo, if you want the work done for you: a dedicated compliance officer runs your program on an open-source platform, for $10,000 for the year, platform and service included. If you have in-house security and want a self-serve tool, look at Drata or Secureframe.
Is there an open-source alternative to Vanta?
Yes. Probo is open source on GitHub and free to self-host, with no vendor lock-in.
What is the cheapest Vanta alternative?
Probo self-hosted is free. With a dedicated compliance officer, it costs $10,000 for the year, platform and service included. Vanta typically costs $15,000 to $25,000 a year before any consultants.
Which Vanta alternative works with AI agents?
Probo. Every record is available through a full GraphQL API, an MCP server with 400+ tools and the prb CLI, so Claude, ChatGPT or Cursor can work on your compliance together with your team.
How fast can I get audit-ready with Probo?
It depends on your setup. A small team with a standard stack can be audit-ready in 2 to 4 weeks, because a compliance officer does the work and follows up with you on the gaps. You don't have to work out on your own whether you're ready to book the audit, how to book it or what the auditor will ask.