Skip to main content Pricing Find the right way to run compliance

Products

Compliance Officer Service Expert-led compliance, end to end Compliance Portal Share security documents securely Document Management Draft, approve, and sign your policies Employee Portal Your whole team’s compliance, in one portal Access Review Monitor user access across all your systems AI Agents Run compliance from the tools you use Cookie Banner Consent that follows every visitor's law Device Agent Continuous security posture for every device Open-source platform Deploy Probo on your own infrastructure

Resources

Customer stories How teams get compliant with Probo Blog Ideas and guidance from the Probo team Compliance Hub Practical compliance guides and free tools Love from customers What customers say about working with Probo
Overview Understand Probo and its core concepts Product Explore Probo's GRC capabilities Developers Explore GraphQL, CLI, MCP, n8n, and webhooks Deployment Probo Cloud, self-hosting, and configuration

Explore

GitHub Explore our open-source compliance tools

Compliance done for you, by a dedicated compliance officer.

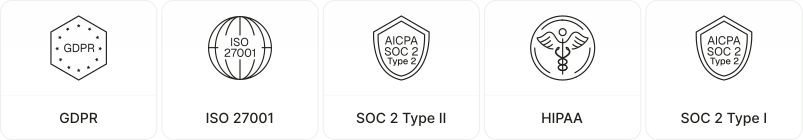
A dedicated compliance officer runs your compliance program for you, from the risk analysis to the audit and all year after, whatever the framework: SOC 2, ISO 27001, HIPAA, GDPR and more.
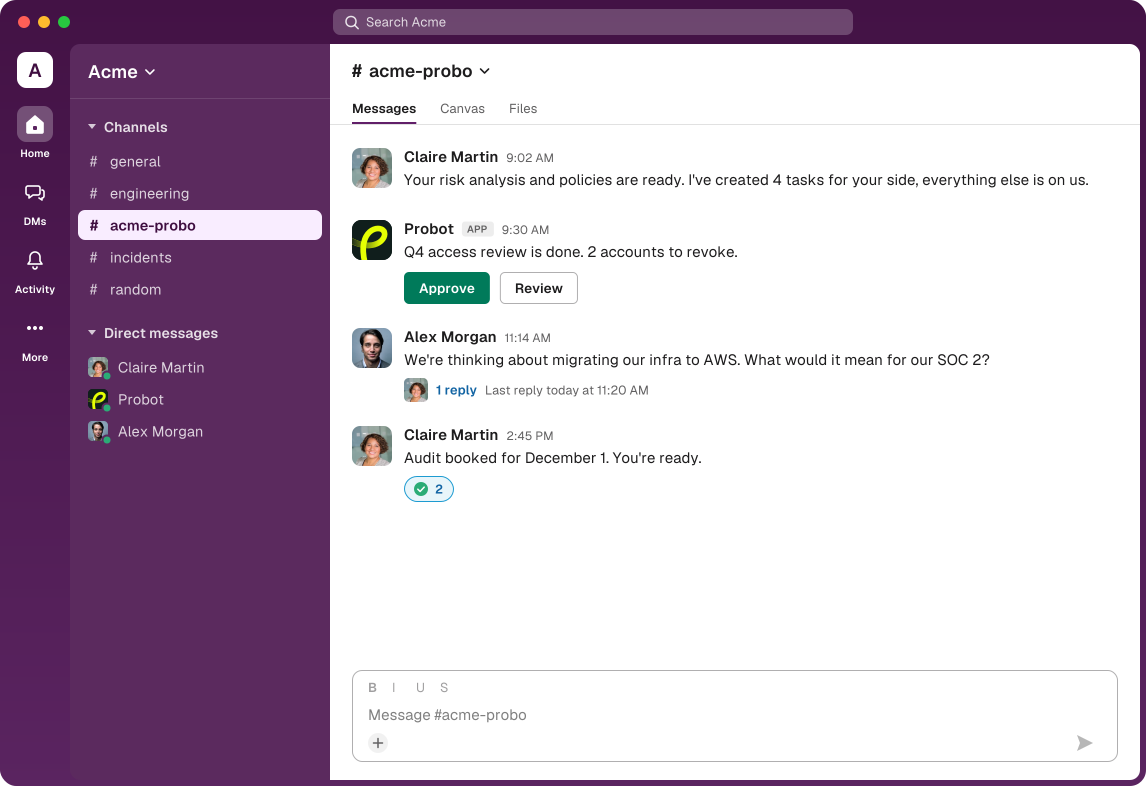
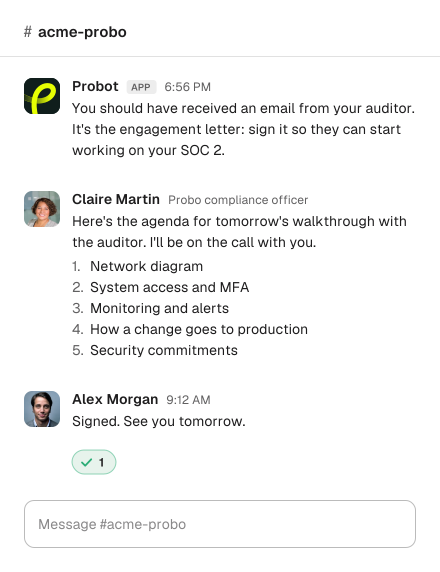
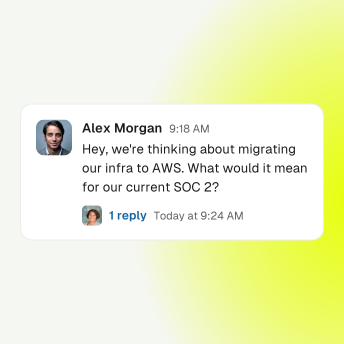
A shared Slack channel where a Probo compliance officer shares ready policies, an access review, an answer to a customer question and the booked audit date

A compliance service that does the work for you.

You don't buy a tool and figure it out. A compliance officer runs your program on Probo's cloud platform, and your team stays on product.

A dedicated compliance officer

A real person who knows your company, reachable on Slack and on calls. Not an AI bot, and not a ticket queue.

A program tailored to your company

Built from a risk analysis of your company and your stack, not from a template handed to every customer.

A legitimate auditor

We recommend an audit firm that fits your company, or work with yours after checking that it is legitimate.

Built for your AI agents

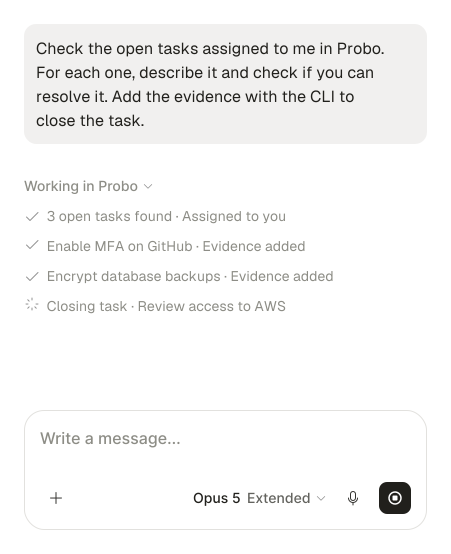
Your own agent can do your side of the work and update Probo through GraphQL, MCP and the CLI.

Run all year, not just until the audit

Access reviews, offboarding checks, policy renewals and new-hire controls are handled for you.

How it works

From the first call to the audit, then all year after: here is what your compliance officer does, and what is left for you.
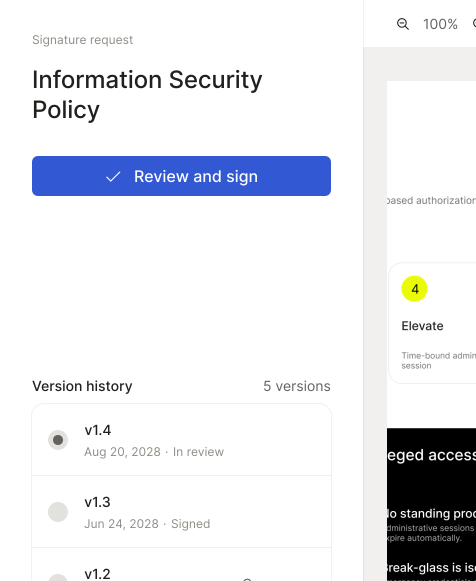
We write your program, for your company

  • One onboarding call to understand your team, your stack and your customers.
  • A full risk analysis, then a gap analysis and a roadmap for your framework.
  • Policies, risk assessment, asset and third-party registers, written for you.
  • We tell you exactly what to do or change on your side, nothing more.

We run the recurring work

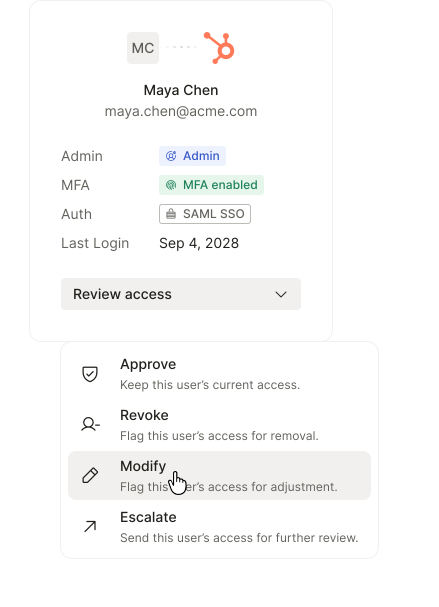
  • Quarterly access reviews, and an access review at every offboarding.
  • Policy renewals and signatures, new-hire and offboarding controls verification, third-party reviews.
  • A quarterly security meeting with your compliance officer to check controls and processes, and keep your compliance documentation up to date over the year.
  • Each finding is validated with you before anything changes.

Your AI agents do your side

  • Every gap becomes a task in Probo, with a ping in Slack.
  • Your own agent can make the change, capture the evidence and update the task through MCP.
  • Your compliance officer reviews what was done. Agents act with the permissions of the person who connected them.

We take you through the audit

  • We tell you when you are ready and book the audit with you.
  • During the audit intro, your officer sits with you as your internal compliance officer.
  • We handle all the back and forth with the auditor during the period, and review the report.
  • You pay the auditor at cost. Probo takes no margin on the audit.

What your compliance officer handles

The recurring work that auditors sample and teams forget, done for you all year.

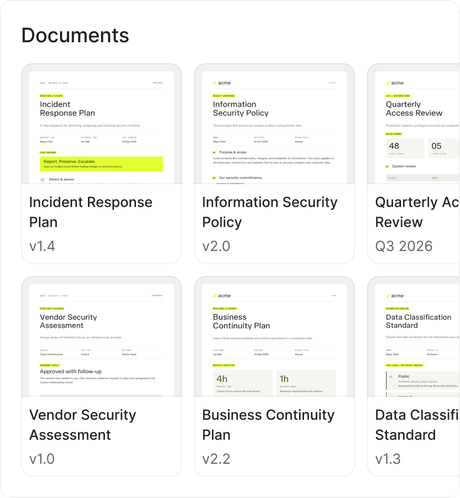
Policies written for you

Your policies describe how your company really works, and are renewed on schedule.

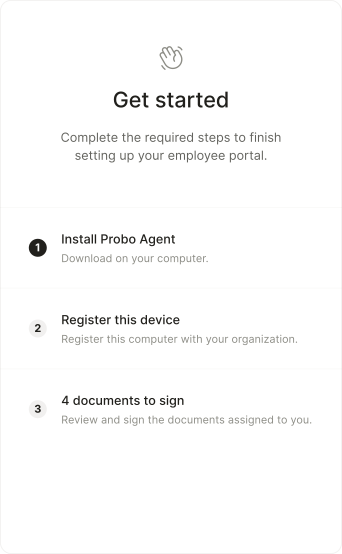
Signatures collected

Your team signs in the employee portal. We follow up so you don't have to.

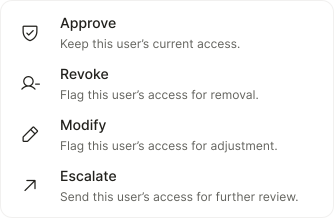
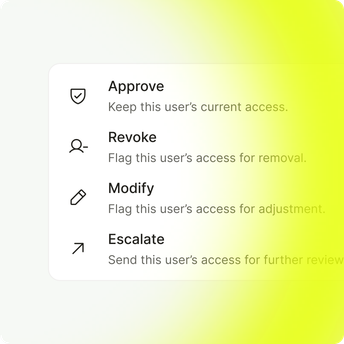
Access reviews

Run every quarter and at every offboarding, with findings validated with you in Slack.

Devices checked

Employees enroll their device in the portal. We alert you on Slack.

Slack, not tickets

Ping us on Slack or book a call for any question or prospect request.

Evidence ready for the auditor

Your officer knows what the auditor will ask for and collects it before they do.

Security questionnaires answered

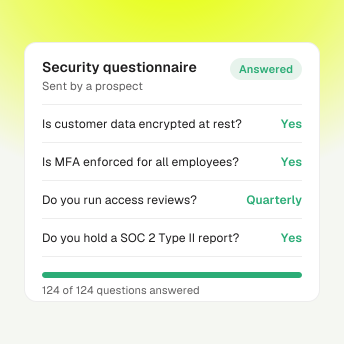
We answer your customers' security questionnaires for you.

Third parties reviewed

We review your vendors and keep their assessments up to date.

Security training provided

We provide security awareness training for your team.

Trusted by 130+ companies

Founders and CTOs hand their compliance to Probo so their team can stay on product.
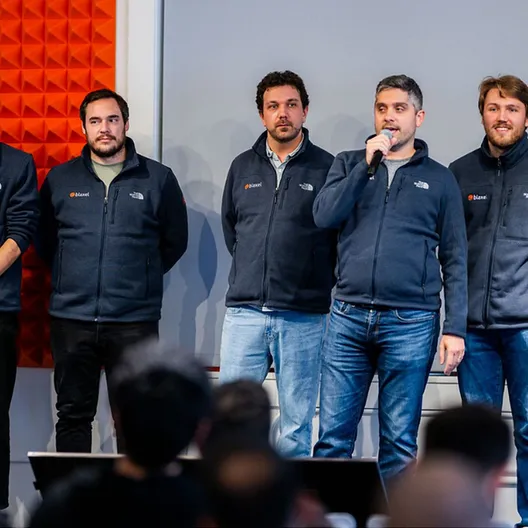
Paul Sinai and the Blaxel team
“Probo handled our SOC 2 and compliance, so we could focus on building.”
Paul Sinai
CEO & Co-founder of Blaxel
Paul Sinai

Trusted by teams who would rather build product

Trace for Good Jimo Lucis Filiz Ahrefs

Questions, answered

Discover what else Probo can do